§ Category
Category

Cyber Tools

CM

Image-Mode Linux Concentrates Persistence Into /etc and /var

Image-mode RHEL and bootc move /usr to a read-only ostree commit and turn host updates into container pulls. That fixes one class of problem and creates a different one for defenders. Here is what actually changes on disk, what to detect, and where the model breaks.
·
AC

TPM-Only BitLocker: The Default Configuration YellowKey Fully Defeats

Chaotic Eclipse dropped two unpatched Windows zero-days on May 13, 2026. YellowKey turns an NTFS transaction log on a USB stick into a BitLocker bypass through WinRE — physical access, no recovery key, no PIN required on TPM-only boxes. GreenPlasma is the companion privilege escalation through CTFMON. No CVEs, no patches, and a researcher who has promised more for June’s Patch Tuesday.

·
Cyber Tools

ClickFix Detection Without the Fairy Tale

ClickFix initial access has been pasting PowerShell into RunMRU for two years and most detection content still treats it like a primer. Here is what the telemetry actually looks like, what tunes out, and where teams keep getting it wrong.

·
Cyber Tools

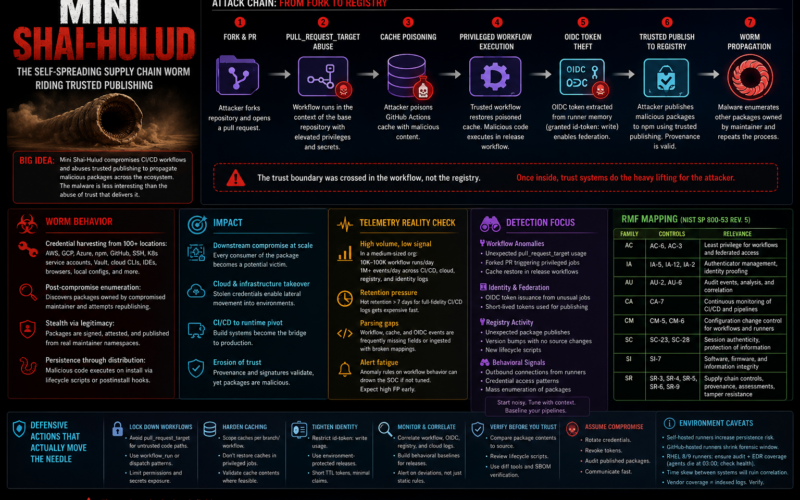
Mini Shai-Hulud and the Collapse of Software Provenance Trust

The uncomfortable part about Mini Shai-Hulud is not the malware itself. Credential stealers are everywhere. Obfuscated JavaScript loaders in npm packages are not exactly new territory either. The problem is that this thing successfully rode through trusted publishing infrastructure and valid provenance paths, which means a lot of the security plumbing people have been congratulating …

·
Cyber Tools

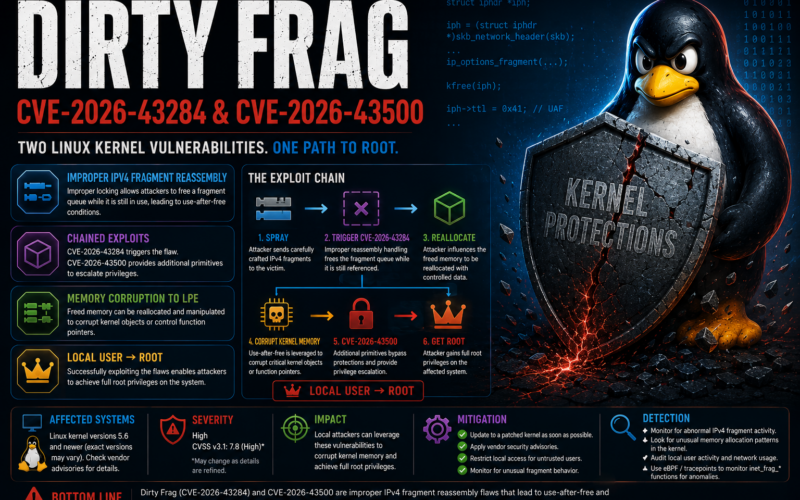
Dirty Frag (CVE-2026-43284, CVE-2026-43500): The Page-Cache Write Class Skips algif_aead and Lands Back at Root

Hyunwoo Kim’s Dirty Frag chain extends the Dirty Pipe / Copy Fail class to skb paged fragments. The xfrm ESP receive path provides a deterministic 4-byte page-cache store (CVE-2026-43284); the rxrpc receive path provides a namespace-free trigger (CVE-2026-43500). One PoC, no race, root on Ubuntu, RHEL, CentOS Stream, AlmaLinux, Fedora, and openSUSE — including hosts that already blocklisted algif_aead for Copy Fail.

·